
The EAM platform where every record is physically verified.
Most EAM deployments fail on the same rock: the data. Records for equipment that no longer exists (ghost assets), real equipment the system has never heard of (shadow assets), and work orders written against both. Keyco gates every record behind a physical identity — an asset exists on the platform because a tag was activated on it — so work orders, maintenance schedules, and lifecycle analytics run on data that matches the floor.
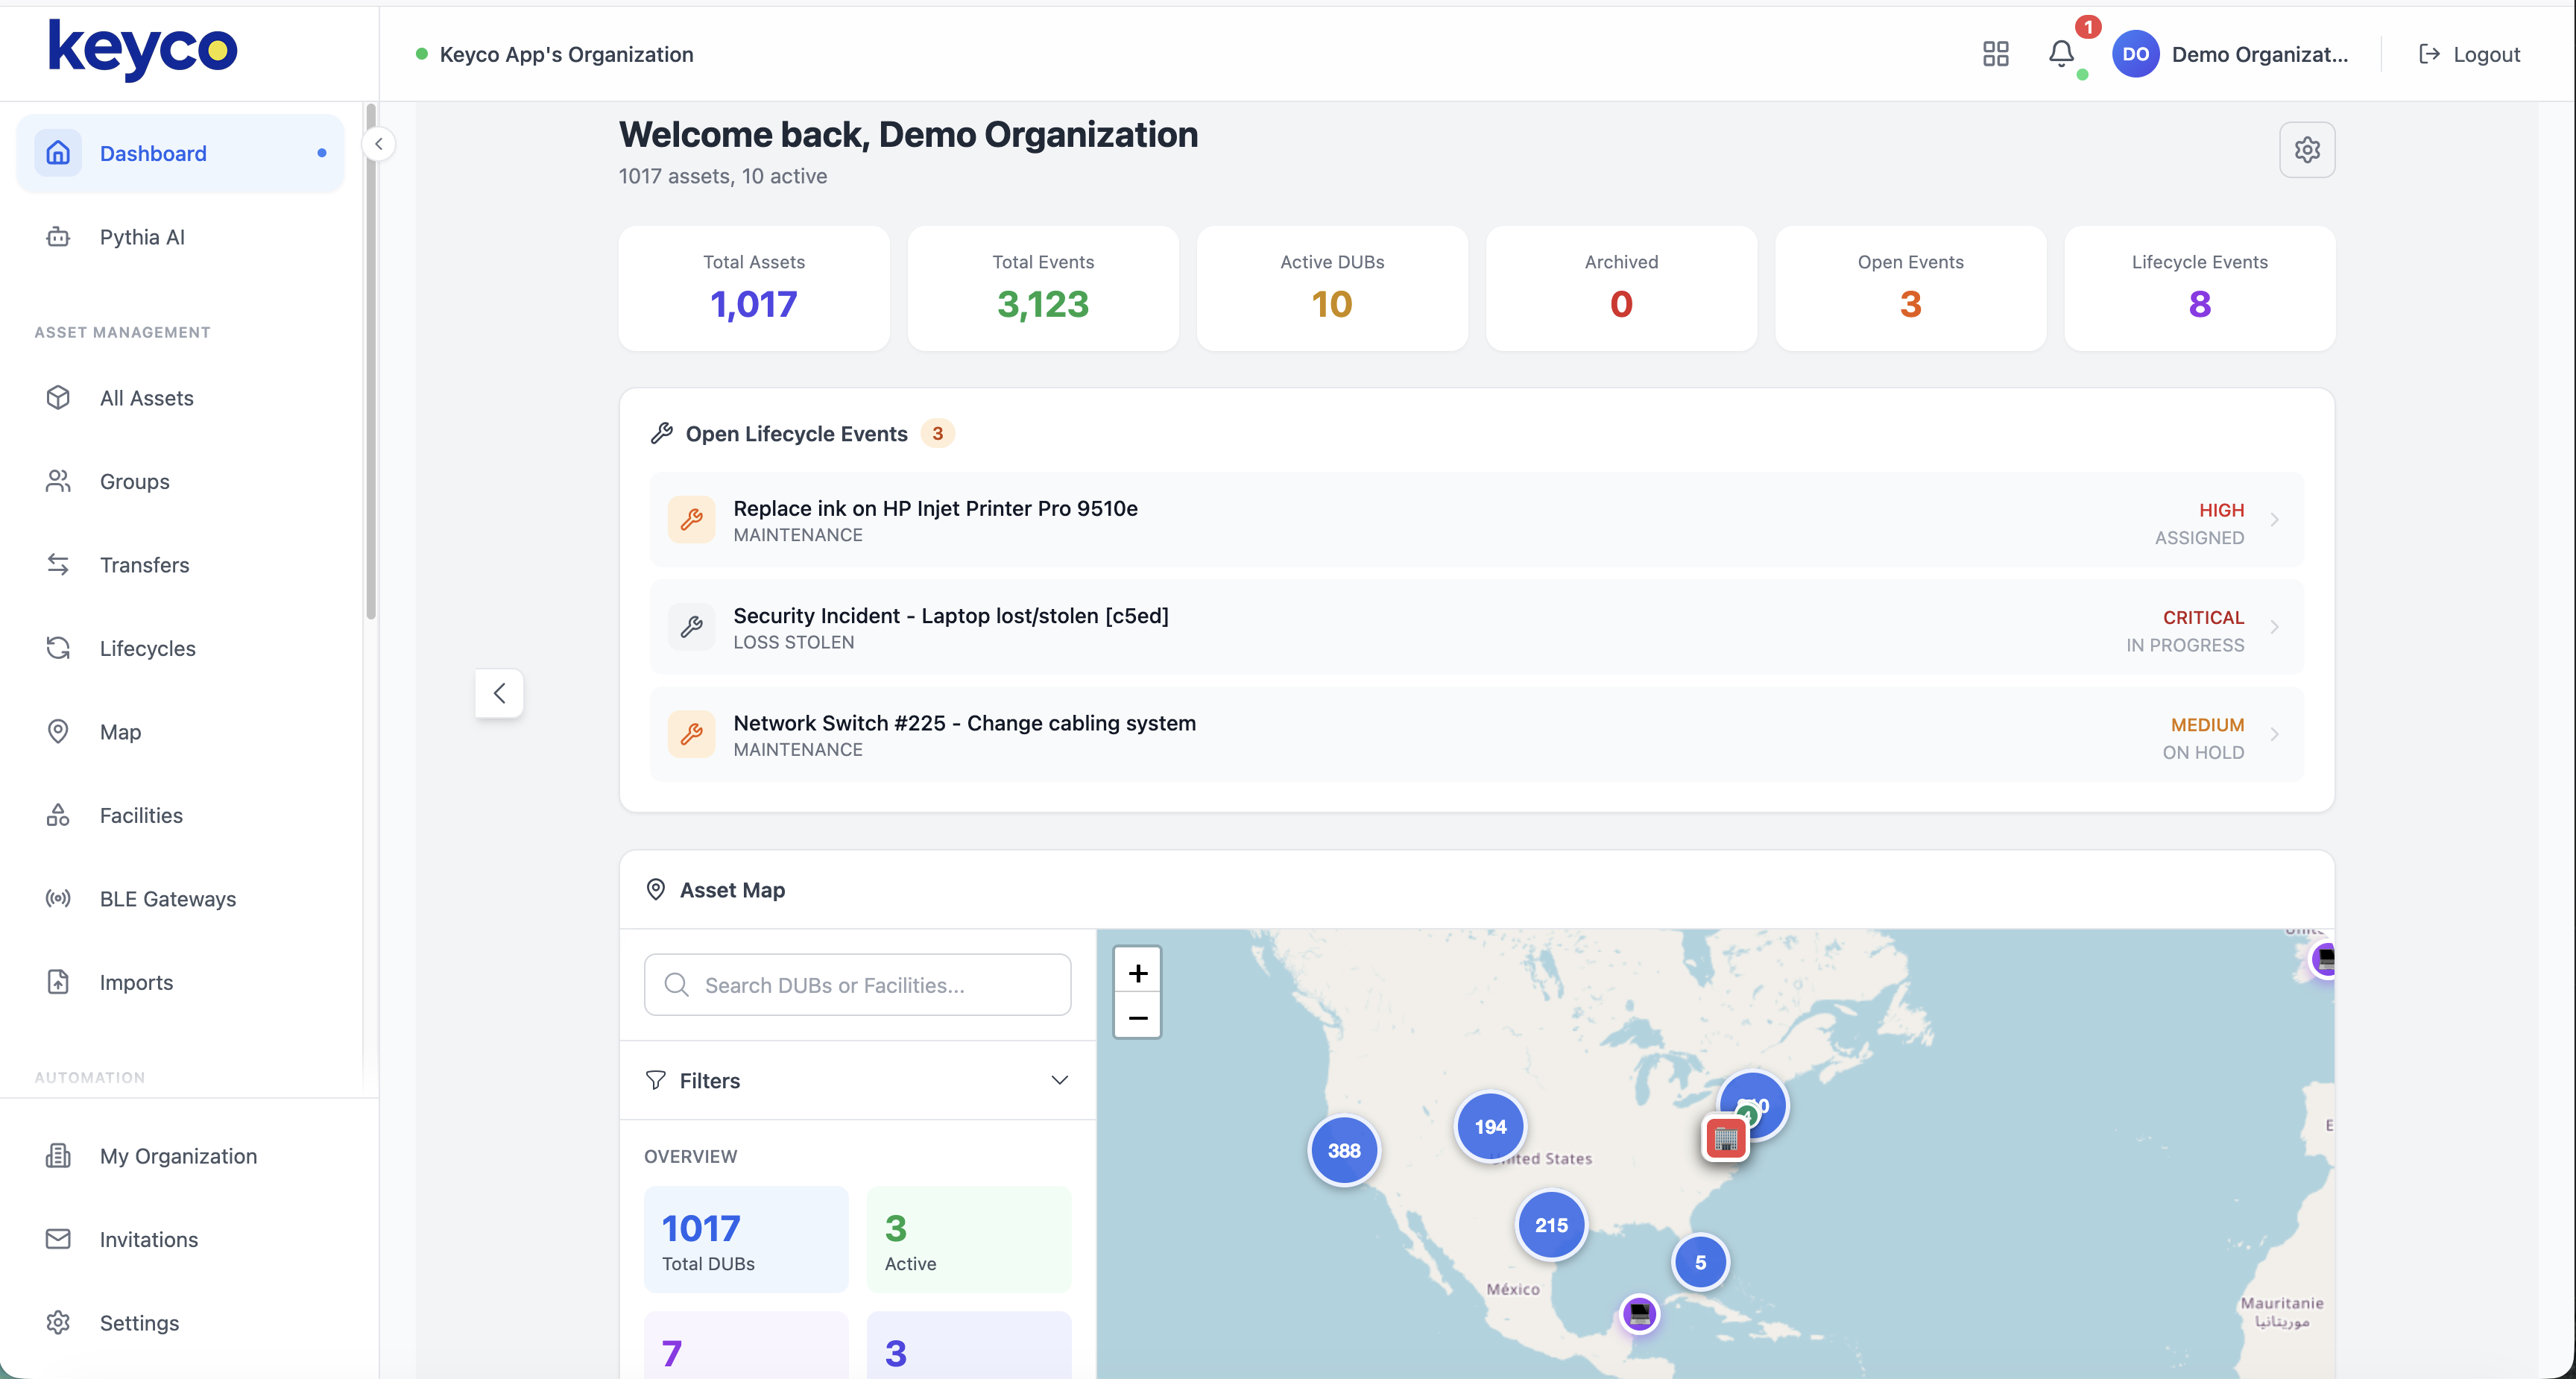
The architecture behind verified EAM:
Physical identity gating
Every DUB carries a platform-controlled unique identity. Asset records can only be instantiated by activating a physical tag — copied codes resolve to the same identity and duplicates are rejected.
Workflow engine with physical proof
Work order steps are confirmed by activating the asset's tag at the asset — QR or NFC — so completion is cryptographically tied to presence, not a checkbox.
Event-driven integration
Every lifecycle event — maintenance completed, custody transferred, asset retired — can fire a webhook in real time. A full REST API (docs.qrdub.com) mirrors data into ERPs and government systems of record.
Role-based access & audit
Granular permissions per role, org-wide audit logging of every change, domain-restricted membership, and full organization data export.
Dual-mode telemetry
Physical tags (QR/NFC/BLE) for equipment and a software agent (Digital DUB) for connected devices — one registry covering both.
Verified asset registry
No manual asset creation. Every record starts with a physical tag on a physical asset — ghost and shadow assets can't exist.
Work orders & workflows
Configurable workflows with physical confirmation at each step — a task is done when someone verified it at the asset, not when a box was ticked.
Preventative maintenance
PM schedules that generate work orders ahead of due dates, with full service history living on the asset itself.
Lifecycle & utilization intelligence
Idle equipment surfaces before you re-buy it. Maintenance trends surface before they become failures. All computed over verified assets.
Reporting & audit trail
A custom report builder, scheduled reports, and an org-wide audit log — every change traceable to a person and a timestamp.
Integration by design
Every lifecycle event can fire a webhook — mirror asset and maintenance data into the ERPs and government systems of record you already run.